 Bayu Permadi
Why Is Your Cloud Infrastructure More Vulnerable Than You Think?
When your company migrates to digital infrastructure, cloud security misconfiguration becomes one of the most real threats, and it often goes unnoticed until major damage has already been done. Many organizations assume that large cloud providers automatically guarantee complete security for all of their data and applications. In reality, the Shared Responsibility Model requires companies to actively manage the security of their own internal configurations. Without a thorough understanding of this, even a small gap such as an open port or an overly permissive access right can become an entry point for malicious actors. This is where proactive risk mitigation becomes a deciding factor in your business continuity in the digital era.
The Hidden Threat Behind Cloud Architecture
This hidden threat is not always a sophisticated cyberattack using cutting-edge malware. More often it is a simple administrative oversight in managing cloud architecture. As a decision-maker, you should be aware that a single misconfigured public storage bucket can trigger a massive Data Breach within minutes. According to global security research from credible institutions such as Gartner, most security incidents in cloud environments are caused by user error rather than by failures on the part of the cloud provider. The complexity of modern architectures, especially multi-cloud setups, often blurs your IT team’s visibility and makes it difficult for them to monitor every asset change in real time. For this reason, building a shared awareness of the importance of a secure cloud architecture is a first step that can no longer be negotiable.
The Real Cost of a Configuration Oversight
When an incident results from this kind of oversight, the cost to the company goes far beyond the direct financial losses from fines or data ransoms. Non-material impacts, such as lost customer trust, damage to a brand reputation built over many years, and strict regulatory sanctions, are often severe blows that are difficult to recover from. For tightly regulated industries such as fintech, healthcare, or e-commerce, non-compliance with data security standards can lead to the permanent revocation of an operating license. Lost productivity from system downtime during forensic investigation also adds a significant operational burden for internal management. Investing in early mitigation and system hardening is far more economical than post-incident recovery, which can drain a company’s valuable resources.
Understanding the Root Cause: Why Cloud Security Misconfiguration Happens
To address this problem effectively, we need to understand why cloud security misconfiguration occurs so frequently in today’s dynamic enterprise environments. One of the main causes is the pace at which developer teams release new features, which often means basic security protocols are overlooked in order to meet market deadlines. When business innovation is prioritized to an extreme over system resilience, security gaps begin to appear one by one without the oversight team noticing. Without centralized controls and architectural standardization, every new code deployment can introduce new vulnerabilities that put the company’s entire digital ecosystem at risk. Balancing release speed with compliance to security protocols should be a primary concern for technology leaders.
The Complexity of Identity and Access Management (IAM)
Incorrect Identity and Access Management (IAM) settings are among the largest contributors to Cloud Misconfiguration incidents today. Many organizations grant excessive administrator access to users or third-party applications for the sake of operational convenience, which is a practice that is not recommended. This violates a basic principle of information security, the Principle of Least Privilege, under which users should have only the minimum access they need. As a result, if a single credential is compromised by an attacker, they can easily escalate privileges and take control of the entire internal network. Managing IAM manually across hundreds of active cloud accounts is a heavy task that calls for a systematic, centralized, and automated approach.
Configuration Drift at Scale
Another problem frequently faced by CTOs and IT Managers is configuration drift. This happens when cloud infrastructure settings that were initially secure gradually change over time because of daily maintenance or emergency fixes made manually. These small, hurried changes are often poorly documented, creating deviations from the original compliance baseline. Without full visibility and reliable automated monitoring tools, your IT team keeps operating in the dark, unaware of new risks. The inability to detect configuration changes instantly is the largest gap that external attackers exploit.
The Human Factor: Fatigue, Training, and Inconsistent Processes
Most configuration errors are rooted in people, not technology. High workloads make IT teams prone to mistakes on repetitive configuration tasks. A lack of training leaves risks unrecognized, and undocumented processes produce security settings that differ from one environment to the next. Standardizing processes, providing regular training, and automating routine tasks are the most effective ways to reduce these errors.
Building a Solid Foundation: Strategies to Address Cloud Security Misconfiguration
Given these complex challenges, companies need to adopt a proactive approach to transform their infrastructure into a resilient system. The solution to cloud security misconfiguration does not lie in adding layers of security software at random, but in integrating security into the entire system development lifecycle. By aligning security (Cloud Security) from the architecture planning stage, you can minimize vulnerability risks before the code runs in production. This is a strategic step toward a business ecosystem that is stable, compliant, and ready to face modern security threats. Security should not be seen as a barrier to speed, but as an enabler of safe business acceleration.
Applying Secure by Design and DevSecOps Automation
Applying the Secure by Design principle means making security the top priority in every cloud architecture decision a company makes. In practice, this is achieved by adopting Infrastructure as Code (IaC) methodology, which allows IT teams to define the entire infrastructure using centralized configuration files. By integrating automated security scanning tools into the CI/CD pipeline, every potential cloud security misconfiguration can be detected from the earliest development phase. This DevSecOps approach not only shortens the time to release applications to market, but also provides assurance that every release meets compliance standards. Through automation, human error, a leading cause of configuration failures, can be reduced to a minimum.
Continuous Auditing Through Cloud Security Posture Management (CSPM)
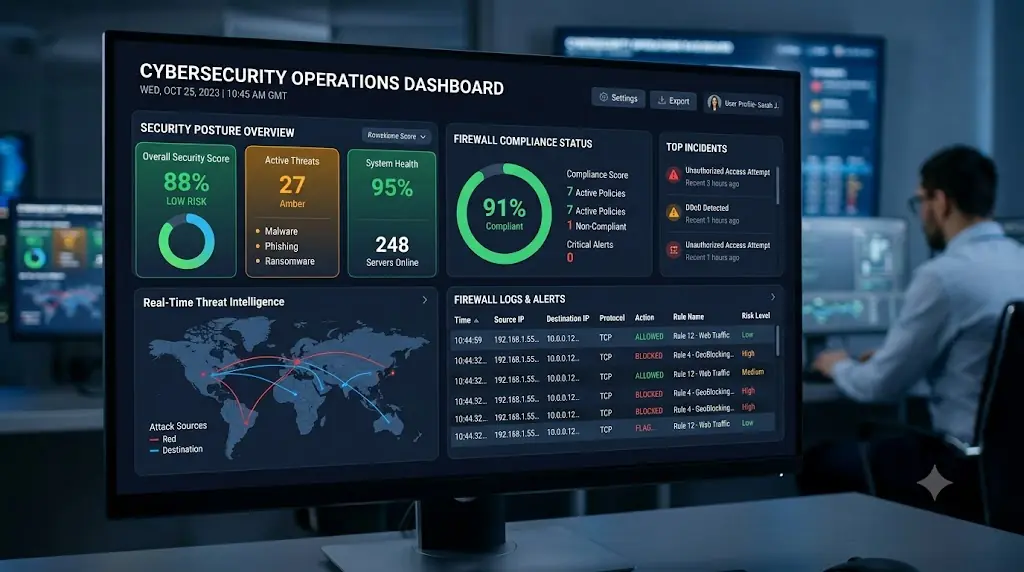
Beyond automation during development, real-time post-deployment monitoring is essential for maintaining system integrity over time in production environments. Cloud Security Posture Management (CSPM) technology allows companies to continuously monitor configuration compliance against international industry standards. These tools automatically identify when a sensitive port is suddenly opened to the public or when a suspicious change is made to an IAM policy. Once an anomaly is detected, a CSPM system can send an instant notification to the security team or even perform automated remediation on its own. Relying on periodic manual audits is no longer relevant in a cloud landscape that changes every second; continuous visibility is the key to defense.
Moving Forward with Pandawa Cloud .Net: Secure Your Business Acceleration
Building and managing a fully secure cloud architecture requires deep expertise, considerable time, and dedicated resources. As your strategic partner, Pandawa Cloud .Net is here to help your company manage this operational complexity without sacrificing the speed of business innovation. We understand that every business has unique needs, so our approach is always tailored to the scale and strategic goals of your organization. With the support of an experienced team of experts, you can focus on growing your core business while we keep your infrastructure secure. We act as a trusted advisor, accompanying every step of your company’s digital transformation safely.
Strategic Collaboration for Comprehensive Infrastructure Protection
Through our comprehensive consulting services, we help you conduct an in-depth assessment of the security posture of your current cloud architecture. We will identify every existing cloud security misconfiguration, develop a structured remediation roadmap, and implement reliable security automation solutions. Working with us is not simply about buying technology services, but about building a long-term partnership to protect your company’s most valuable digital assets. Contact our team of experts today to discuss in depth how we can help you build a resilient cloud infrastructure. Together with Pandawa Cloud .Net, let us build a digital foundation that is secure, efficient, and ready to support your business growth in the future.