 Bayu Permadi
Note: This case study is an illustrative scenario built on challenges that businesses commonly face. The company name, figures, and results are examples only and do not represent any specific client.
Navigating Regulatory Uncertainty and Information Security in the Fintech Industry
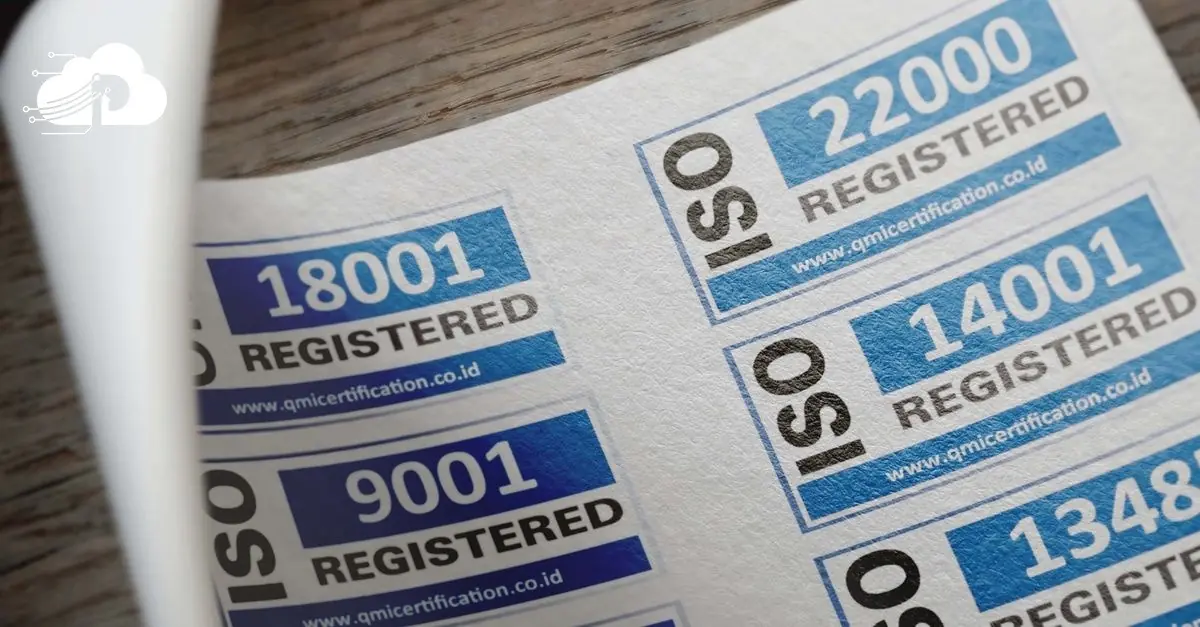
In a fast-moving financial technology industry, studying the ISO/IEC 27001 standard through an ISO 27001 fintech case study is a valuable strategic step for decision-makers. As a policy-maker in your organization, you know that customer trust and regulatory compliance are the most important currencies in the modern financial ecosystem. Information security audits are often seen as exhausting, bureaucratic, and a potential brake on product innovation. Yet ignoring the standard is the same as leaving the door wide open to a data breach that could destroy your business’s reputation overnight.
Navigating Tight Financial Regulation in the Digital Era
The Financial Services Authority (OJK) and Bank Indonesia continue to tighten their oversight of the information technology infrastructure used by fintech players. Every startup is expected not only to deliver innovative financial solutions, but also to prove that it operates a robust information security management system. Without a formal certification such as ISO 27001, your company will face real difficulty when trying to expand into broader markets or form strategic partnerships with conventional financial institutions. Compliance is no longer just a supporting piece of legal paperwork. It is an absolute prerequisite for surviving and competing in an industry that is highly sensitive to security risk.
The Reality of Compliance Challenges for Fintech Startups
Many mid-sized fintech startups are caught in a dilemma between speed to market and meeting rigid security standards. Conventional certification often takes nine months or even a year, which is far too long for a business that moves in weeks. A shortage of people with specialized information security expertise makes matters worse, pushing engineering teams to work extra hard outside their core competence. As a result, certification projects are often delayed, costs balloon, and the business’s main focus becomes fragmented and loses direction.
How the Fintech Startup XYZ Achieved ISO 27001 in a Short Time
Cutting certification time from years to just three months is not a coincidence. It is the result of precise planning and the right cloud architecture. Through an in-depth analysis of this ISO 27001 fintech case study, we can see how a focused, risk-based approach can eliminate the redundant processes that often slow down audits. The key lies in integrating internal governance policies with reliable cloud infrastructure automation. By applying these principles, the fintech startup XYZ showed that strict compliance can be achieved efficiently without sacrificing the operational agility of its developer teams.
Breaking Down the Main Barriers to Fintech Compliance
Before beginning its transformation, FinTech XYZ faced a classic problem: policy documentation that was out of sync with the technical implementation on the ground. Each internal audit uncovered security gaps in user access rights management, as well as a lack of real-time log activity monitoring. A comprehensive review of these issues made clear that the foundation of their previous cloud infrastructure had not been designed to support compliance with international standards. The challenge called for a fundamental change in how they handle sensitive customer data: strictly separating development and production environments, and implementing robust end-to-end encryption.
A 3-Month Acceleration Methodology Toward Certification
In the first month, the focus was entirely on an in-depth gap analysis to identify the differences between the existing state and the ISO 27001 standard. In the second month, the team began infrastructure remediation by migrating sensitive workloads to a standardized cloud platform with built-in security controls. Security policy automation was applied rigorously, so every configuration change could be tracked automatically, without manual intervention that is prone to human error. By the third month, the internal audit and the first stage of the external audit ran smoothly because all compliance evidence had been neatly documented and was instantly accessible to auditors.
Turning Compliance from a Cost Center into a Competitive Advantage
Key Lessons from This ISO 27001 Fintech Case Study
Looking more closely at this ISO 27001 fintech case study, the most striking aspect is the shift in mindset from compliance as a burden to compliance as a powerful business lever. Earning certification within three months gave the entire internal team a significant morale boost and raised the company’s credibility in the public eye. FinTech XYZ now has a much stronger negotiating position with large banking partners and institutional investors who demand high security standards. This outcome shows that investing in secure, regulation-ready cloud infrastructure can return multiple times its value to the business over the long term.
Competitive Advantage in the Eyes of Investors and Regulators
Applying the framework from this ISO 27001 fintech case study shows that fast compliance can shorten business-to-business (B2B) sales cycles significantly. Strategic partners no longer need to run months-long security due diligence, because an ISO 27001 certificate is already a globally recognized assurance of quality. In front of regulators, your company will be seen as a mature, responsible business with a strong commitment to consumer protection. This not only makes it easier to obtain new operating licenses, but also lowers the risk of administrative sanctions or financial penalties resulting from poor data management.
Standardized Cloud Infrastructure as the Core Foundation
This kind of accelerated compliance is hard to achieve without cloud infrastructure designed to meet strict security standards. By using a cloud platform that makes full use of the shared responsibility model, the workload on your IT team for managing physical controls and the server environment can drop significantly. Essential security features, from next-generation firewalls and intrusion detection systems (IDS) to data encryption key management, are already natively integrated. This lets your engineering team stay focused on developing core product features without worrying about the complexity of low-level security configuration.
Strategic Steps to Start Your Company’s Information Security Transformation
The first step to replicating the success of the ISO 27001 fintech case study we have discussed is to evaluate the readiness of your current cloud infrastructure. You do not have to go through the compliance journey alone, relying on costly trial and error and risking a failed audit. Pandawa Cloud .Net is a strategic partner that can help your company design, implement, and manage cloud infrastructure fully aligned with the ISO 27001 standard. With a structured approach and an experienced team, we help you save time and resources as you work toward your compliance targets.
Building a Compliance Foundation with Pandawa Cloud .Net
We understand that every fintech company has its own system architecture and business needs, so a one-size-fits-all approach will never work. Through our integrated cloud compliance consulting services, we help you map security controls precisely at the cloud infrastructure layer. We make sure that every aspect, from identity management (IAM) and activity log monitoring to the Disaster Recovery Plan, is implemented according to industry best practices. This way, when external auditors arrive, your systems are ready and well documented.
Schedule a Strategic Cloud Security Consultation
Do not let regulatory compliance hold back business growth and technology innovation at your fintech company. Take a proactive step today by discussing the specific challenges your IT and compliance teams are facing with our senior consultants. We will help you map out a compliance roadmap that is realistic, efficient, and directly improves the trust your business earns in the market. Contact the Pandawa Cloud .Net team to schedule a strategic discussion session, and let us build a solid cloud security foundation together.