 Bayu Permadi
Facing the Reality of Data Risk in a Dynamic Multi-Cloud Era
Why Is Traditional Security No Longer Enough in Cloud Environments?
In today’s digital business landscape, protecting company data is no longer just a matter for the IT department. It is a core pillar of business continuity. The shift to modern infrastructure calls for ISO 27001 cloud compliance as the gold standard for ensuring comprehensive information security across your entire digital ecosystem. Traditional security approaches that rely on physical perimeters or on-premises firewalls are no longer adequate when data is spread across dynamic, decentralized cloud environments. Many companies fall into the mistaken assumption that their cloud provider automatically secures all of their data assets, when the shared responsibility model requires active involvement from your own organization. Without a solid understanding of this governance, security gaps will remain wide open to cyber threats that grow more sophisticated every day.
The Financial and Reputational Impact of Failed Data Protection
Failing to protect sensitive customer data does not only result in technical disruption such as operational downtime. It can also cause severe, systemic financial damage to a corporation. With strict regulations now in force, such as Indonesia’s Personal Data Protection Law (UU PDP), legal sanctions and administrative fines are a real risk that can directly threaten a company’s financial stability. Rebuilding customer trust after a data breach costs far more than the upfront investment in a robust, standardized defense. Decision-makers such as CEOs and CTOs increasingly recognize that compliance with international standards is no longer an optional extra for corporate image. It is a critical risk-mitigation instrument for protecting market value and long-term credibility.
Understanding the Strategic Value of Modern Information Security Governance
Aligning Information Security Governance with Global Standards
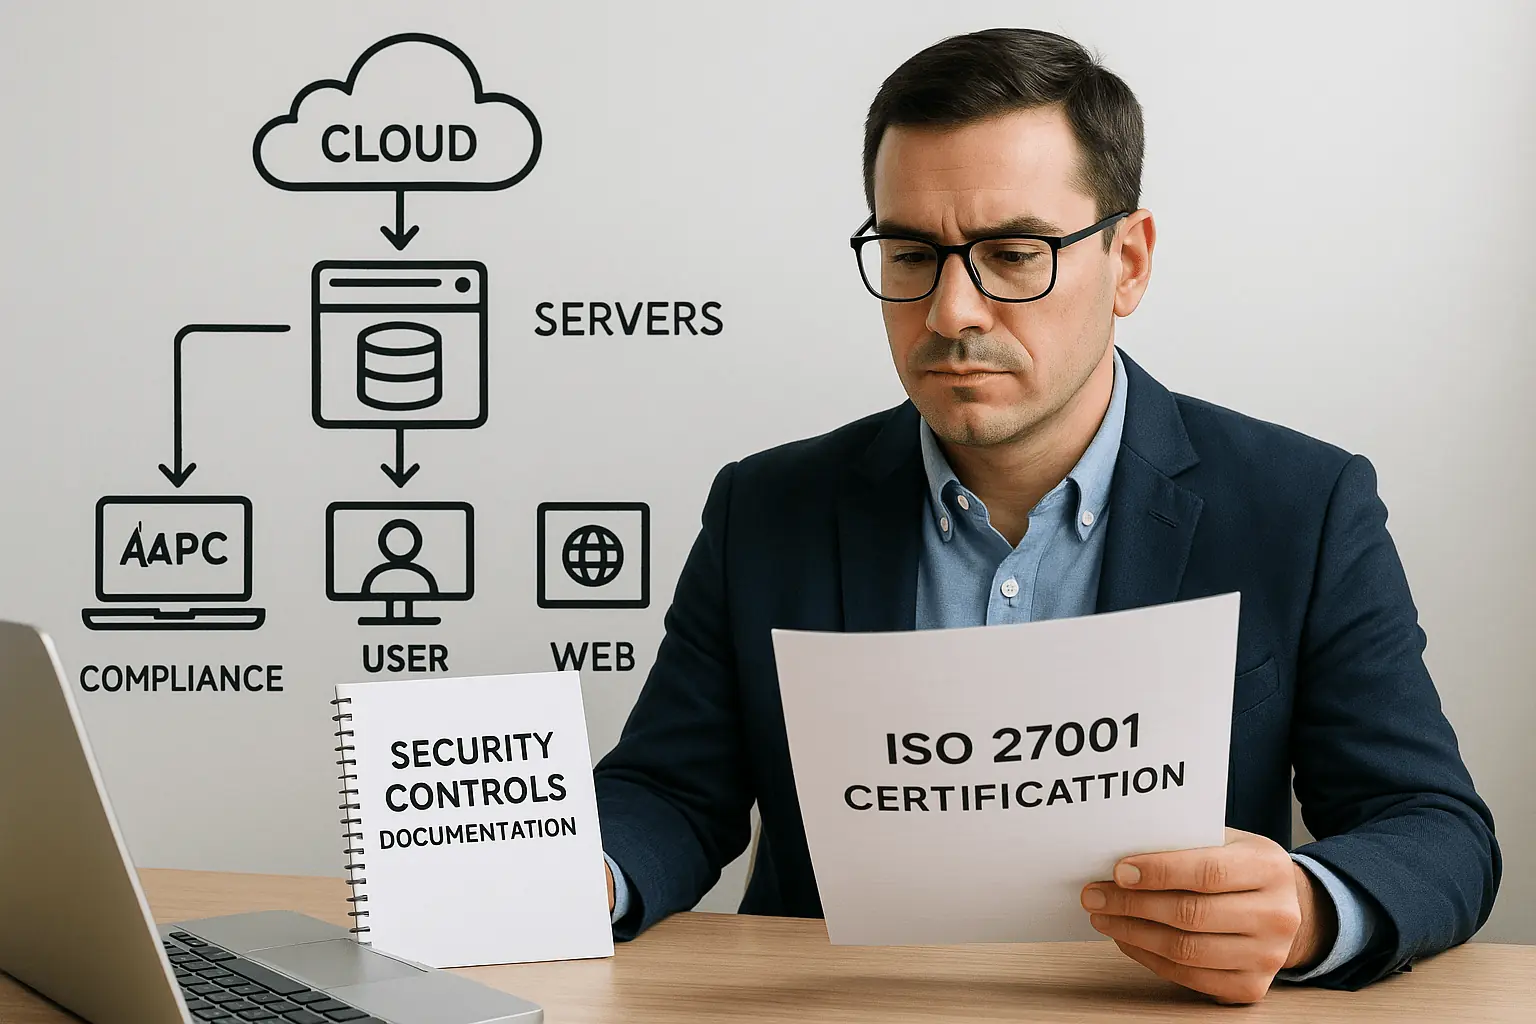
Implementing ISO 27001 cloud compliance gives you a systematic framework for identifying, managing, and minimizing information security risks in a consistent and measurable way. This global standard, published by the International Organization for Standardization (ISO), helps organizations build security into every business process and daily workflow. With this approach, information security is no longer seen as a cost center that strains the budget. It becomes a strategic business enabler that strengthens your negotiating position with large enterprise clients. Compliance also ensures that every internal policy, from user access control to sensitive data encryption, operates in line with internationally recognized standards across industries.
How Risk Management Changes the Way Your Infrastructure Operates
The key to meeting this standard is an organization’s ability to identify its digital assets and regularly evaluate the threats facing them. A structured risk management process allows your IT team to make strategic decisions based on real data, rather than reacting after a security incident has already damaged your systems. With ISO 27001 cloud compliance in place, every configuration change to your cloud infrastructure goes through a rigorous, well-documented security review. This proactive approach significantly reduces the likelihood of human error, which is often the leading cause of data breaches in both public and private cloud environments.
Building Stakeholder Trust Through Standardization
Practical Steps for Implementing ISO 27001 Cloud Compliance
Starting the path to certification requires a clear picture of your current infrastructure, built through a thorough gap analysis. This first step is essential for identifying which security controls are already working well and which critical areas still need improvement or adjustment. A Statement of Applicability (SoA) is then prepared to define the specific ISO 27001 Annex A controls that are relevant to your operational needs and your company’s particular business model. The whole process requires strong leadership commitment from the board and ongoing training for all employees, so that awareness of information protection becomes part of the company’s working culture.
Choosing a Local Infrastructure Partner with Recognized Certifications
For companies operating in Indonesia, choosing a local cloud provider that already holds ISO 27001 certification is a strategic way to speed up your own internal audit. Through this collaboration, you can remove much of the audit burden for physical infrastructure, because the security controls at that layer have already been formally validated by an independent certification body. Pandawa Cloud .Net is a trusted partner that understands why ISO 27001 cloud compliance matters for your long-term growth and operational continuity in a competitive domestic market. With local infrastructure designed to meet strict regulatory standards, we are ready to support your compliance team in simplifying the complexity of information security governance in the cloud.
Practical Steps to Secure Your Business’s Future
Start Assessing Your Infrastructure’s Security Gaps Today
The most decisive first step does not have to be a radical overhaul of your entire system architecture. It can begin with an objective assessment of the security gaps that exist today. A thorough review of identity access, data encryption management, and backup procedures will give you a transparent view of how ready your organization is for a real audit. Postponing this evaluation only increases your exposure to cyber risk, which can disrupt daily operations and damage the credibility you have built over many years. Choosing to act now will put your company several steps ahead of competitors in compliance readiness and digital resilience.
Working with a Wise Peer for a Smooth Audit Readiness Process
Navigating information security regulation in the cloud era calls for guidance from an experienced partner who can act as a trusted strategic advisor (wise peer) to your business. At Pandawa Cloud .Net, we do not only provide high-performance local cloud infrastructure. We also work alongside you to design a digital ecosystem that is secure, compliant, and operationally efficient. We believe that ISO 27001 cloud compliance is not a rigid end goal, but an ongoing journey to keep raising your security standards and the trust of your stakeholders. Let’s have an in-depth conversation with our expert team to shape a compliance strategy that is adaptive, efficient, and matched to your organization’s future growth.